
Audio By Carbonatix
The Cyber Security Authority (CSA) has issued an urgent technical advisory to organisations across the country, warning of a large-scale cybercrime campaign known as “FortiBleed” that is actively targeting Fortinet FortiGate firewalls and Secure Socket Layer (SSL) Virtual Private Network (VPN) gateways.
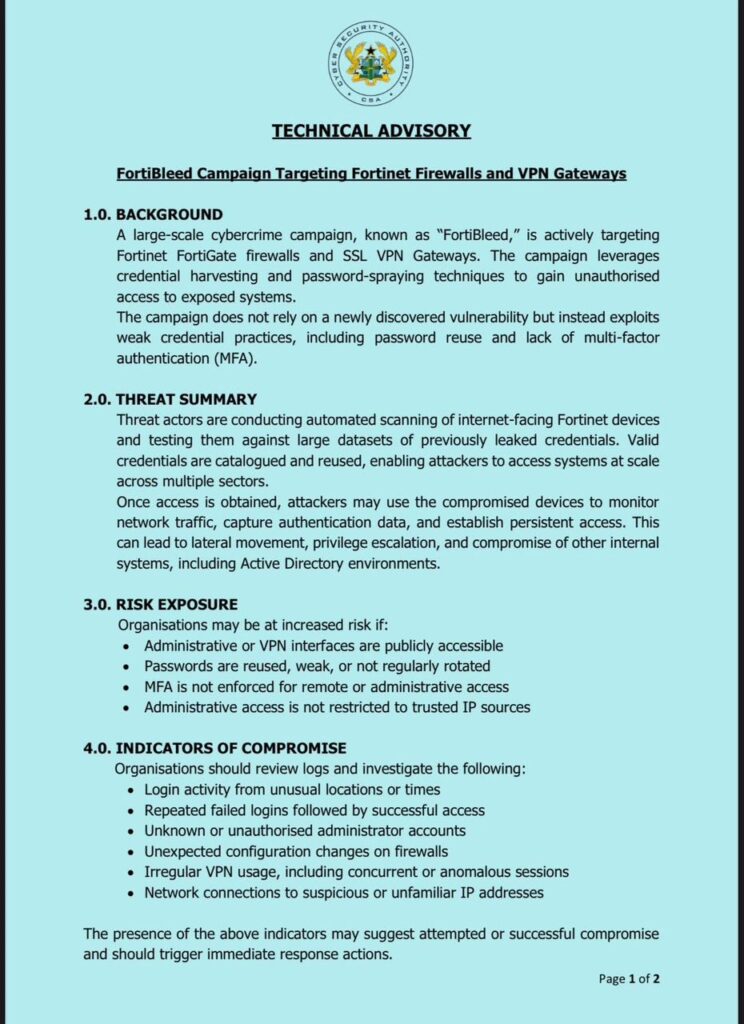
The advisory, released on June 19, 2026, cautioned that the campaign poses significant risks to organisations whose digital infrastructure relies on Fortinet security devices, particularly where weak passwords, password reuse and inadequate authentication measures exist.
According to the CSA, the campaign is not exploiting a newly discovered software vulnerability but is instead taking advantage of poor cybersecurity practices, including weak credentials and the absence of multi-factor authentication (MFA).
Automated attacks
The CSA explained that threat actors behind the campaign are conducting automated scans of internet-facing Fortinet devices and testing them against large databases of previously leaked usernames and passwords.
“Valid credentials are catalogued and reused, enabling attackers to access systems at scale across multiple sectors,” the advisory stated.
It warned that once access is gained, cybercriminals could monitor network traffic, capture authentication information and establish persistent access to compromised systems.
The CSA further noted that successful breaches could lead to privilege escalation, lateral movement within networks and the compromise of additional systems, including Active Directory environments that often form the backbone of institutional IT infrastructure.
Organisations at risk
The advisory identified several conditions that increase an organisation’s vulnerability to the FortiBleed campaign.
These include publicly accessible administrative or VPN interfaces, the use of weak or recycled passwords, failure to enforce multi-factor authentication for administrative access, and unrestricted access to administrative systems from untrusted internet sources.
The CSA said organisations operating critical digital infrastructure, including those in government, finance, telecommunications, education, healthcare and other essential sectors, should pay particular attention to the warning.
Warning signs
To help organisations identify potential compromises, the CSA outlined a number of indicators that warrant immediate investigation.
Among them are login attempts from unusual geographic locations or at unusual times, repeated failed login attempts followed by successful access, the appearance of unknown administrator accounts, unexpected configuration changes on firewalls and suspicious network connections to unfamiliar internet addresses.
The CSA stressed that the presence of any of these indicators may suggest attempted or successful compromise and should trigger immediate incident response procedures.
Recommended measures
As part of its mitigation strategy, the CSA urged organisations to immediately rotate all administrative and VPN credentials, enforce multi-factor authentication and ensure the use of strong, unique passwords.
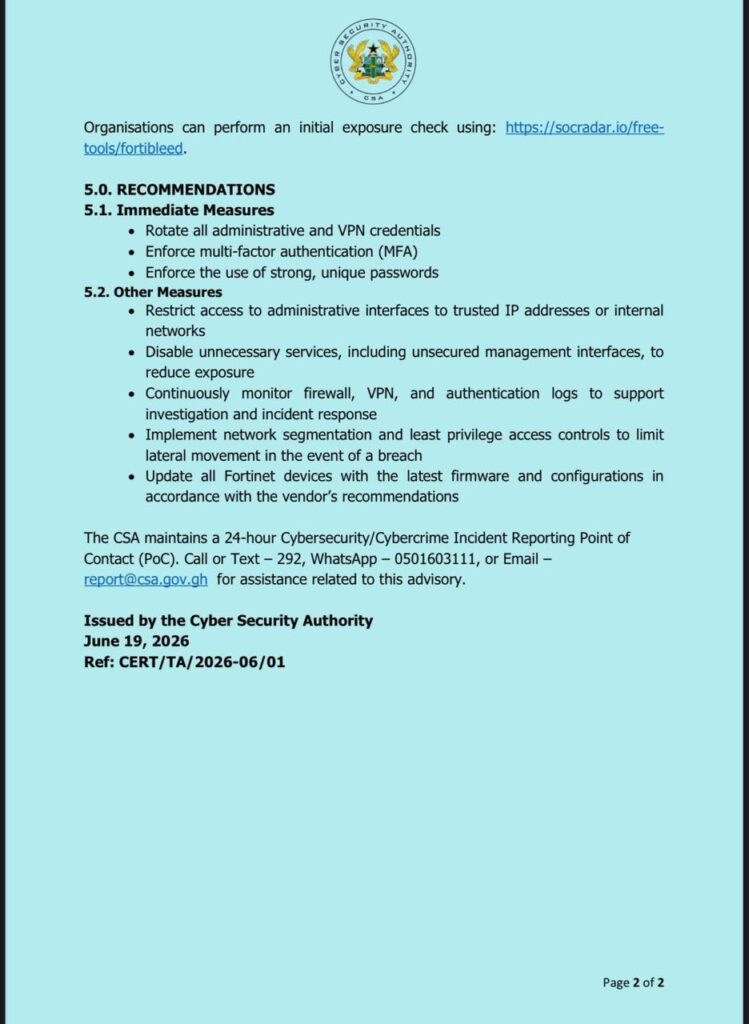
Additional recommendations include restricting access to administrative interfaces to trusted IP addresses or internal networks, disabling unnecessary services and unsecured management interfaces, and continuously monitoring firewall, VPN and authentication logs.
The Authority also advised organisations to implement network segmentation and least-privilege access controls to limit the spread of attacks in the event of a breach.
Furthermore, all Fortinet devices should be updated with the latest firmware and configurations in accordance with vendor recommendations.
To assist organisations in assessing their vulnerability, the CSA directed users to perform an initial exposure check through publicly available cybersecurity assessment tools.
The CSA reiterated its commitment to supporting organisations facing cybersecurity incidents and encouraged affected entities to promptly report suspicious activity.
Growing cyber threat landscape
The latest advisory comes amid increasing concerns about the sophistication and frequency of cyberattacks targeting organisations worldwide.
Cybersecurity experts have repeatedly warned that attackers are increasingly exploiting stolen credentials and poor security hygiene rather than relying solely on software vulnerabilities.
The CSA has, in recent years, intensified public awareness campaigns and regulatory interventions aimed at strengthening the country's cyber resilience, particularly among operators of Critical Information Infrastructure (CII).
The CSA maintains a 24-hour Cybersecurity and Cybercrime Incident Reporting Point of Contact and has urged organisations experiencing any suspicious activity related to the FortiBleed campaign to seek immediate assistance.
Latest Stories
-
Fuel prices may rise, but GOIL says 30% transport fare hike doesn’t add up
6 minutes -
Minority questions why alleged masterminds behind US$350m cocaine haul remain free
7 minutes -
AGI calls for workplace training to boost youth employability
13 minutes -
Mahama inspects proposed site for Upper West Regional Airport
17 minutes -
Government recruits 16,000 health personnel to support FPHC programme – Health Minister
22 minutes -
GOIL sets Sept. 16 deadline for decision on fuel prices
24 minutes -
Mahama reiterates government’s commitment to end double-track SHS system
27 minutes -
TMA warns against illegal felling of trees in Tema
32 minutes -
Bagbin urges Ewe diaspora to convert cultural network into investment platform
37 minutes -
Ghana Battalion 92 returns home after Lebanon peacekeeping mission
47 minutes -
The Pitt is up for 25 Emmys – but the show’s biggest fans are real-life doctors
58 minutes -
Four alleged illegal sand winners remanded
1 hour -
Unemployed man gets 18 months imprisonment term for causing harm
1 hour -
Amazon pauses work with cargo firm after fatal crash
1 hour -
Vice President pushes greener Ghana after floods expose cost of environmental neglect
2 hours