

Audio By Carbonatix
The Cyber Security Authority (CSA) has called for faster sharing of cyber threat intelligence among banks, fintechs, telecommunications companies, regulators and law enforcement agencies to prevent cyberattacks from spreading across Ghana’s digital finance ecosystem.
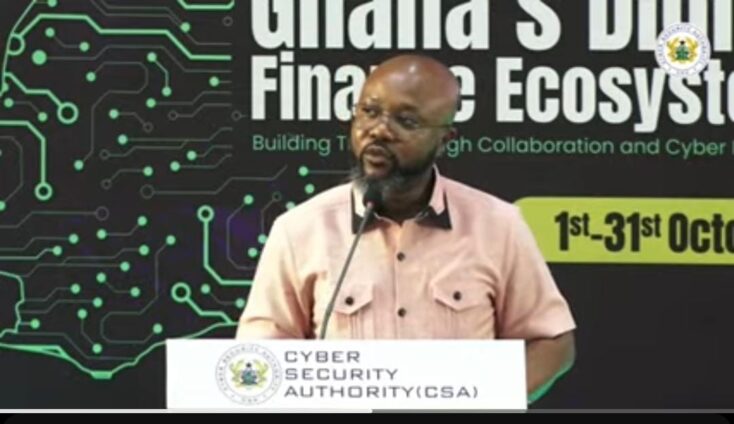
Director-General of the CSA, Divine Selasie Agbeti, said cybercriminals do not operate within institutional boundaries and often exploit gaps between organisations to carry out attacks.
Speaking at the launch of the 2026 National Cyber Security Awareness Month (NACSAM), Mr Agbeti said institutions must therefore move beyond individual cybersecurity efforts and develop a more coordinated response to emerging threats.
He stressed that financial and digital institutions must be able to exchange actionable information quickly enough to detect and disrupt attacks before they result in financial losses.
“We need financial institutions to share actionable threat intelligence. We need telecommunications companies to work closely with banks and fintechs,” he said.
“We need regulators, technology companies, law enforcement agencies, and cyber security service providers to exchange information quickly enough to disrupt attacks before losses occur.”
According to him, the interconnected nature of Ghana’s digital economy means that a cyberattack on one institution can quickly become a threat to other businesses and their customers.
“Cyber criminals do not operate within our institutional boundaries. They do not care whether an incident involves a bank, a fintech, a telecommunications company, a regulator, or a law enforcement agency. They exploit the gaps between our institutions. Our response must therefore be equally connected,” he said.
Mr Agbeti argued that the effectiveness of collaboration should not be measured by the number of agreements signed between institutions, but by how quickly they can identify, communicate and respond to threats.
“The real measure is how quickly we can detect, share, respond, and recover together,” he said.
He further warned that delayed information sharing could result in institutions repeatedly falling victim to the same cyber threats.
“If one institution detects an attack today, and another experiences the same attack tomorrow, because intelligence was not shared, we have collectively failed,” he said.
The CSA Director-General also urged boards and senior executives of financial and technology companies to treat cybersecurity as a business and economic risk rather than an issue that should be left solely to information technology departments.
“Cyber security must not remain buried somewhere in the technology departments. Cyber risk is a business risk,” Mr Agbeti stated.
Latest Stories
-
Government seeks $165m to complete operational phase of Boankra Integrated Logistics Terminal
8 minutes -
‘Show us the evidence’ – Upper West teachers demand proof of arrears payments
14 minutes -
GH¢1 D-Levy suspension will offer relief to fuel consumers – COPEC
15 minutes -
Youth Olympic Games in Africa: policy, regulation, and perspectives on shaping youth lives
22 minutes -
Contractors move to site for construction of 120-bed trauma hospital in Bole – Kwakye Ofosu
30 minutes -
Poor institutional leadership hindering Ghana’s creative industry – Oscar Provencal
42 minutes -
CSA demands faster sharing of cyber threat intelligence among financial institutions
58 minutes -
CSA warns Ghanaians to verify money requests as AI makes online fraud harder to detect
1 hour -
NEIP CEO urges Africa to build systems that turn ideas into businesses
1 hour -
Global Organised Crime Index says cybercrime is undermining Ghana’s digital sector
1 hour -
Global Organised Crime Index says fraud and tax evasion are widespread across Ghana’s economy
1 hour -
Threats to journalists limit coverage of cocaine trade in Ghana – Global Organised Crime Index
1 hour -
Kumawu MP commissions 4-unit nurses’ quarters at Bodomase
1 hour -
Two arrested after suspected narcotics intercepted at Kasoa
1 hour -
All our pipe stock is gone — Duraplast Marketing Manager counts losses after Avenor fire
1 hour